--:--
ping —
download —
upload —

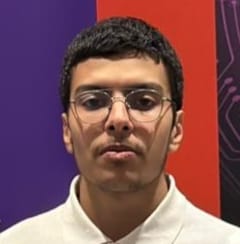
Mohamed Aziz Rahmouni

~/Whoami

Name
Mohamed Aziz Rahmouni
Role
Network & Telecommunications Engineering Student
Focus
Digital ForensicsPenetration TestingMobile RE

Defend by day, break by night.

~/Background

Three tracks I actively work in, and train others on.

~/Experience

VamiSec GmbH

Cybersecurity Consultant

October 2026–present

Blue team operations, digital forensics and incident response (DFIR).

  • Work on threat detection, digital forensic investigations, incident response, and mitigation.
  • Design an AI solution to support threat detection, DFIR workflows, and mitigation.
Smart Skills

Penetration Tester Intern — cybersecurity division of TAC TIC Group

Jul–Aug 2026

Offensive security for enterprise clients, from reconnaissance to exploitation to evidence-backed reporting.

  • Active Directory: mapped attack paths across enterprise forests, Kerberoasting, AS-REP roasting, constrained and Resource-Based delegation abuse, ACL and GPO exploitation, silver and golden ticket scenarios, and lateral movement chains (WinRM, PsExec, RDP hops) up to domain dominance.
  • Web applications: assessed APIs and web apps against the OWASP Top 10, SQLi/NoSQLi, XSS, CSRF, SSRF, IDOR and broken access control, JWT flaws, insecure deserialization, upload validation bypasses, and logic flaws in auth and checkout flows.
  • Validated impact with proof-of-concept exploitation, then translated findings into prioritized, client-ready reports with reproduction steps and hardening guidance.

Securinets

Technical Instructor, Digital Forensics — first national cybersecurity association in Tunisia

Sep 2024–present

Teaching and building the community, one artifact at a time.

  • Contributed to Cybersphere, Tunisia's largest cybersecurity congress, and the ICO 2026 International Cybersecurity Olympiad program.
  • Helped run flagship national CTFs like Darkest Hour and hands-on learning events like CyberCamp across the country.
  • Designed and operated containerized challenge infrastructure sustaining 100% uptime for 400+ participants per event.
  • Delivered hands-on secure-coding and binary exploitation workshops to students from 10+ universities.
  • Authored exploitation and reverse engineering challenges modeling real-world memory-safety and logic flaws.
  • Led the digital forensics track, workshops, CTF authoring, and everything in between.

FL1TZ

CTF Player — Tunisian CTF team

Competitive team play and challenge authoring, podiums, international finals, and everything in between.

  • Full-spectrum CTF play across jeopardy and attack/defense formats, binary exploitation, web, forensics, reverse engineering, and crypto.
  • Authoring original challenges for regional and national competitions, from chained web exploits to live forensics stations.
  • Team lab culture, shared attack notes, internal trainings, and weaponized tooling that everyone deploys.
  • Flying the FL1TZ flag at international finals, CSAW CTF and CSAW Hack My Robot (NYU Abu Dhabi, UAE), Black Hat MEA, ASCWG (Egypt), and the Tech Olympics (Iran).

INSAT

ICT Engineering Student

2023–2028

ICT engineering program covering computer networks, operating systems and kernel-level internals, distributed systems, software and systems engineering, embedded systems, and information systems security, the full stack between the silicon and the network edge.

~/Achievements

podiums & top finishes
  • 1STCyberTEK 3.0 · Team FL1TZ · Tunisia
  • 1STSpooky CTF · Team FL1TZ · Tunisia
  • TOP 3CSAW CTF Finals · Team FL1TZ · NYU Abu Dhabi, UAE
  • TOP 10Tech Olympics Finals · Team FL1TZ · Iran
  • 4THBrunner CTF · Team Choufli 7al
  • 5THSecurinets Finals · Team FL1TZ · Tunisia
international finals · qualified
  • CSAW CTF Finals 2026 · NYU Abu Dhabi, UAE
  • CSAW Hack My Robot Finals 2026 · NYU Abu Dhabi, UAE
  • Black Hat MEA Finals 2025 · Saudi Arabia
  • ASCWG Finals 2025 · Egypt
  • CSAW CTF Finals 2025 · NYU Abu Dhabi, UAE
  • Tech Olympics 2025 · Iran

~/Recent-Posts

Fresh writeups and articles, hot off the bench — hover to pause the feed, or open the full blog for everything.

ad · pentest · internship 4 min read

From 0 to Domain Admin

During these last two days of my internship I ran an internal pentest mission at a company, where I mainly focused on...

read post

browse the full blog — all categories